Cognyte | HUNTICS Network Detection and Response
by Cognyte
HUNTICS NETWORK DETECTION & RESPONSE HUNTICS NDR leverages behavioral machine learning and AI- driven investigation to identify advanced persistent threats from sophisticated adversaries. By combining signature matching, heuristic analysis and machine learning informed by our expertise in nation-state threats, HUNTICS NDR uncovers both known and novel threats, delivering deep network visibility for swift detection and response. HUNTICS NDR goes beyond legacy solutions like IDS by using network data—the most objective source of truth—to address novel threats, while also performing signature-based detection. Our solution offers real-time visibility into network activities, detecting anomalies and patterns that may indicate a compromise, such as unusual data flows or uncommon communication patterns. It continuously analyzes network traffic framed as MITRE ATT&CK tactics, techniques, and procedures (TTPs), enabling swift containment of attacks through ad hoc or automatic response actions.
As a leader in cyber defense and intelligence, Cognyte (NASDAQ: CGNT) draws upon decades of expertise in national security and advanced threat environments to deliver a cutting-edge NDR solution. Our analytics-driven approach can uncover even the most elusive threats and sophisticated threat actors.WHY CHOOSE HUNTICS NDR? DEEP VISIBILITY SOPHISTICATED ACTOR DETECTIONSTREAMLINED, EFFECTIVE RESPONSE Get the full picture of your organization’s assets, with deep and comprehensive visibility across your entire network. Identify and map relationships and dependencies for each asset.Uncover any threat, from common tactics to advanced, stealthy attacks. Our proprietary sensor is designed to catch what others miss, including novel threats from sophisticated nation-state actors. Swiftly respond to threats with user-controlled actions for maximum flexibility and extensibility. Integrate seamlessly with virtually any SOC system, including SOAR. THE SOLUTIONCapture clear and encrypted network data without packet loss, generate metadata logs, and analyze data for known and unknown threats both retrospectively and in near real time, using anomaly and pattern analysis, signatures and MITRE ATT&CK TTPs. Our open and accessible analytics algorithms can be fine-tuned (by users or as a professional service) to fit your organization’s unique needs. Integrate with SOC systems such as SIEM, SOAR, EDR and firewalls to facilitate swift and seamless endpoint containment and remediation. Our scalable solution supports networks of all sizes and types, offering flexible deployment options for on-premise environments.
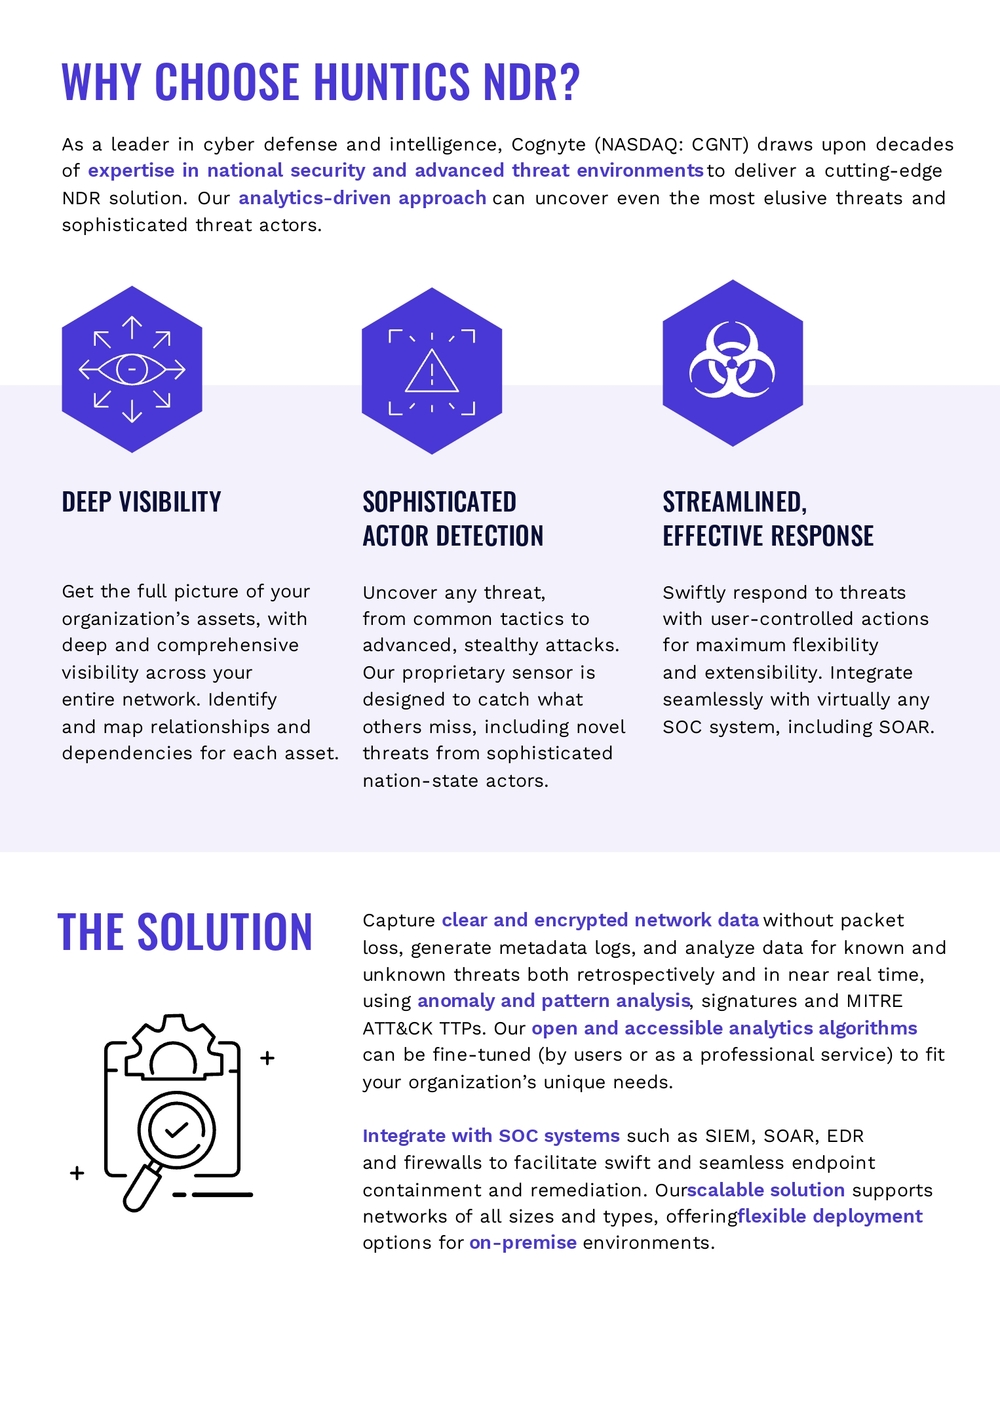
HUNTICS NDR SOLUTION HIGHLIGHTS AUTOMATED INVESTIGATIONS TUNABLE ANALYTICS RETROACTIVE DETECTIONFocus on the most likely attack scenario, rather than individual alerts and leads, with automatically generated attack storylines.Customize and create analytics tailored to your organization’s specific needs and threat attributes. Conduct retroactive searches of known attacks using long-term profiles to determine whether zero-day threats have been seen on the network.RAPID INCIDENT RESPONSE Integrate smoothly with other SOC systems to streamline incident response without relying on IT resources. Data Sources On-Prem SourcesLog Sources PACKETS/LOGSSensors Software Agent Appliance3rd Party CTI Feedsx Analytics AI/ML Behavioral Analysis Signatures Entity ProfilesHUNTICS NDRExternal Intelligence Case Sync Alerts/ Logs Response Actions IoCs PCAP FilesSOAR / EDR / FW / TIPSIEM / XDR StorageSOC Systems Evidence Network Logs File Hashes Captured Packets
Advanced Threat Detection Detect virtually any threat, even low-and- slow APT group attacks, by identifying patterns of behavior consistent with APT TTPs.Enhancing SIEM & XDR Improve SIEM and XDR capabilities with advanced threat hunting, machine learning and behavioral analysis, effectively replacing legacy IDS. Fingerprinting Encrypted Connections Enhance detection and visibility by calculating encrypted traffic hashes and providing decoded metadata from protocol headers. for fingerprinting encrypted connections: Perform on-demand decryption of TLS protocols with user-provided keys.Forensic Analysis Facilitate in-depth investigations to understand attack methodologies, pinpoint threat hunting efforts, collect evidence and prevent future incidents. Adaptability for Evolving Threats Rapidly detect and address emerging threats with flexible, fully-accessible analytics algorithms and Cognyte’s specialized sensor.Near Real-Time Monitoring Benefit from rapid, comprehensive detection and visibility across the entire network. On-Demand PCAP Retrieval Swiftly retrieve specific communication sessions for forensic analysis, while saving time and obtaining precise data without external recordings.Reduce Alert Fatigue Prioritize alerts according to risk and context, minimizing noise and enhancing the efficiency of investigations. USE CASES DETECT MORE, IDENTIFY EARLY, RESPOND FASTER. Contact us to see a demo: NDR@cognyte.com | www.cognyte.com About Cognyte Cognyte is the global leader in investigative analytics software that empowers a variety of government and other organizations with Actionable Intelligence for a Safer WorldTM. Use of these products or certain features may be subject to applicable legal regulation. Users should familiarize themselves with any applicable restrictions before use. These products are intended only for lawful uses by legally authorized users. Not all features may be available in all jurisdictions and not all functionalities may be available in all configurations.Unauthorized use, duplication, or modification of this document in whole or in part without the prior written consent of Cognyte is strictly prohibited. By providing this document, Cognyte is not making any representations regarding the correctness or completeness of its contents and reserves the right to alter this document at any time without notice. Features listed in this document are subject to change. Contact your Cognyte representative for current product features and specifications. 2024 Cognyte